Frequently Asked Questions
Risk Prioritization & Vulnerability Management
How does Ordr prioritize vulnerabilities across my assets?
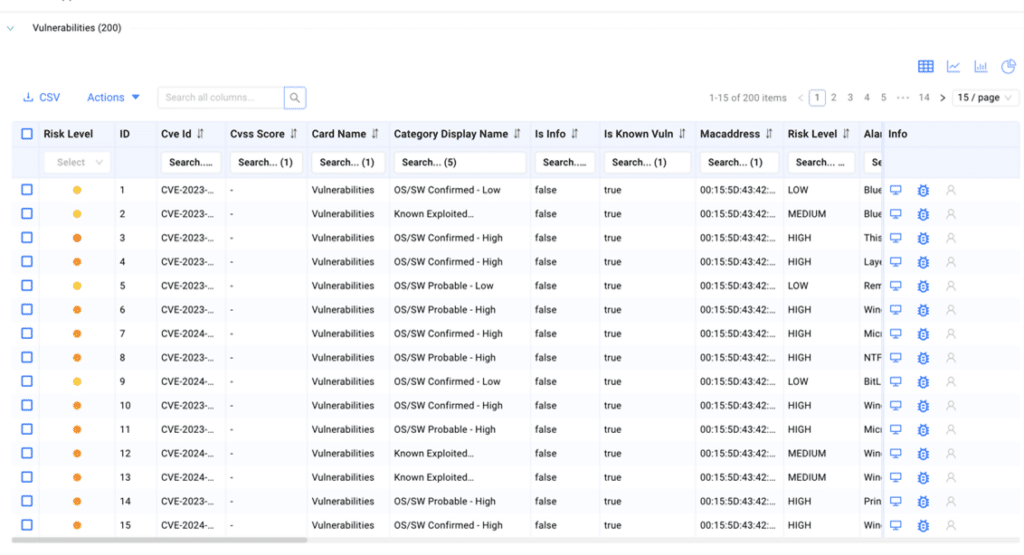
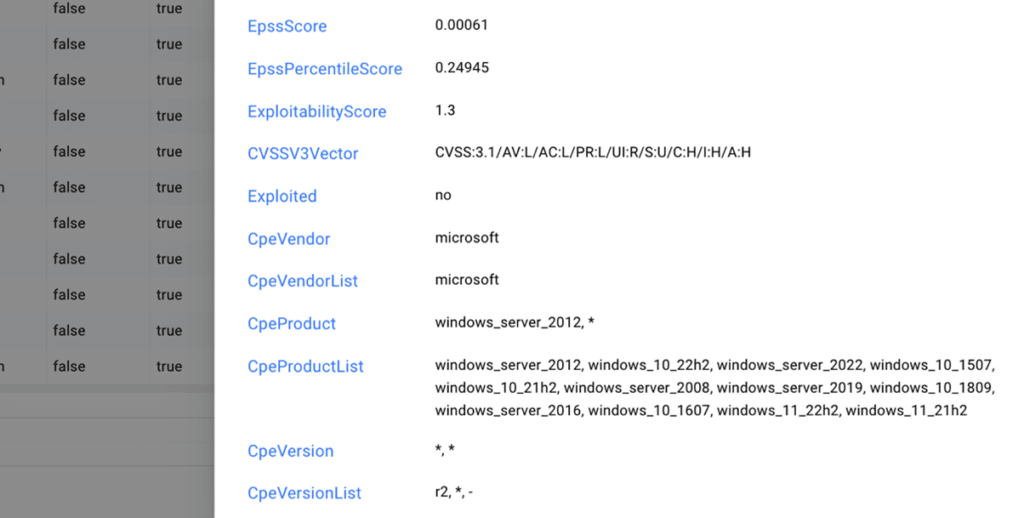
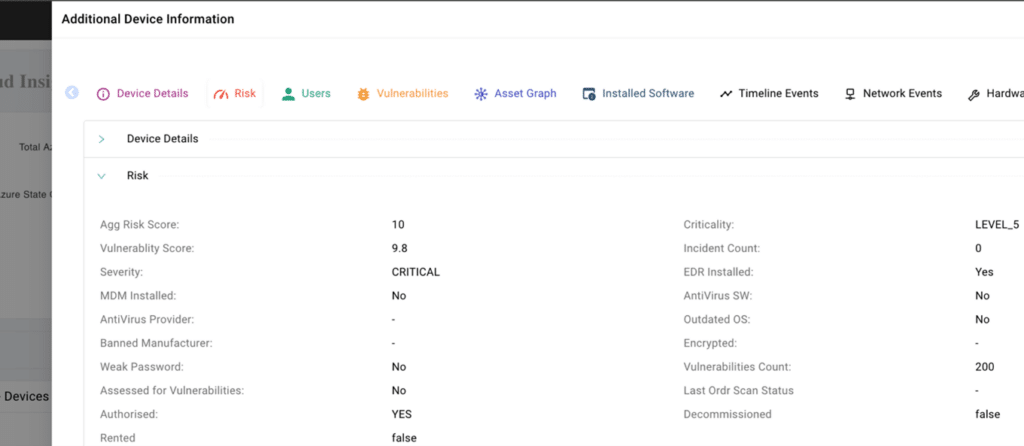
Ordr's Cyber Asset Attack Surface Management (CAASM) product uses AI/ML technology to classify assets and assign business context, enabling risk-based prioritization. Vulnerabilities are scored based on asset context, CVSS scores, exploitability, data type, and location. Each asset receives a risk score from Level 1 to Level 5, with mission-critical assets designated as Level 5. Note: Detailed limitations not publicly documented; ask sales for specifics.
What methods does Ordr use to discover and assign vulnerabilities?
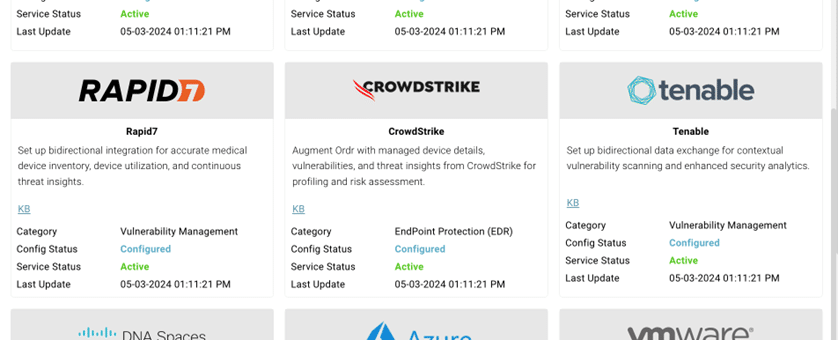
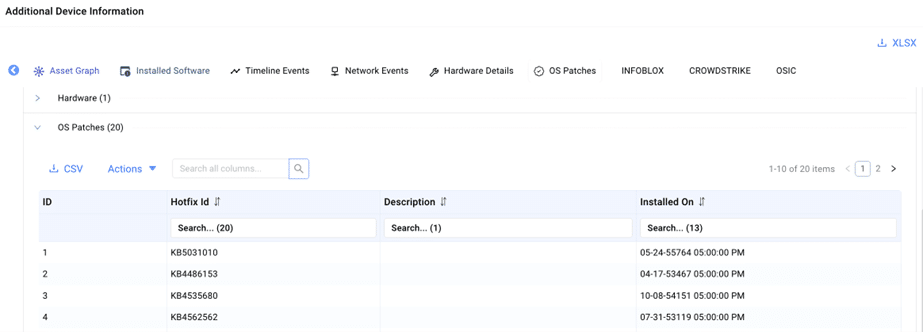
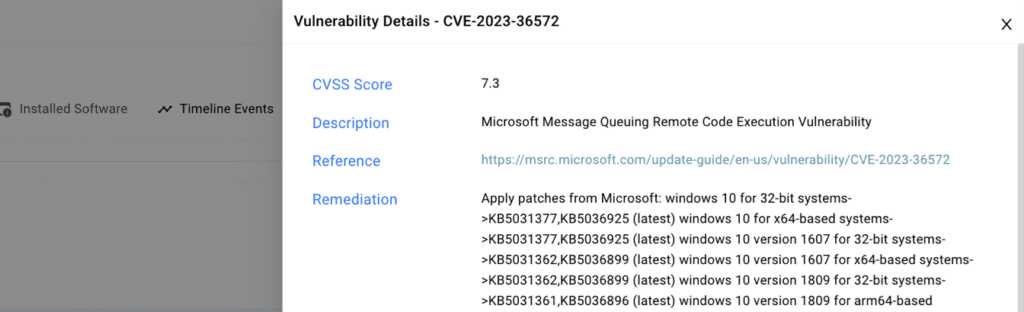
Ordr collects vulnerability data from multiple sources, including integrations with Rapid7, Tenable, and Qualys for regularly scanned assets. For assets that cannot be scanned, Ordr's Software Inventory Collector detects vulnerabilities based on KB/HF correlation. For assets with outdated operating systems, Ordr uses passive and active scanning to collect detailed context and assign vulnerabilities. Note: Coverage depends on integration and asset type; legacy assets may require manual validation.
How does Ordr help reduce alert fatigue for security teams?
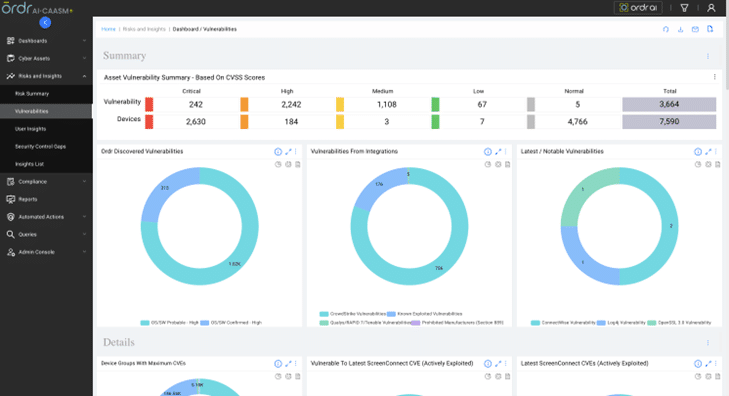
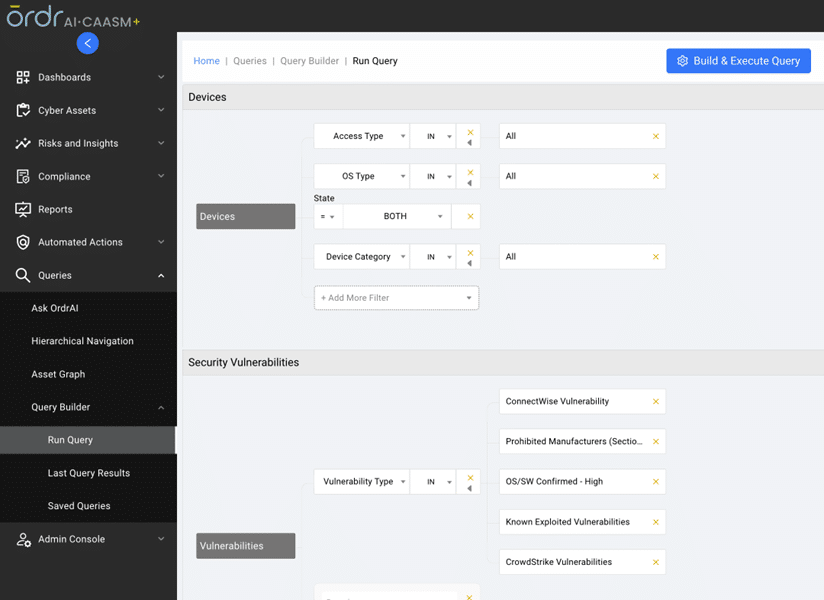
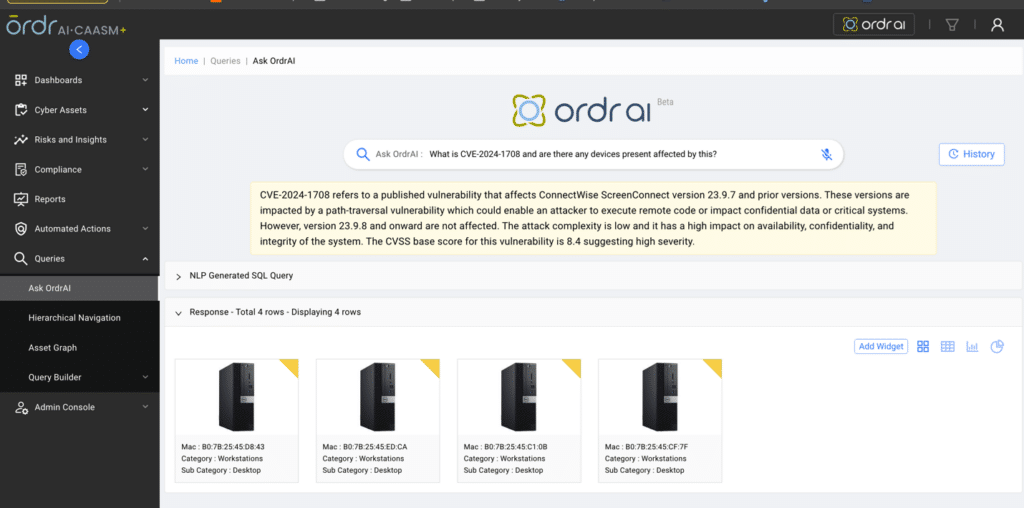
Ordr's AI/ML mapping and correlation engine aligns technical and business priorities, delivering a prioritized list of top risks. Features like the Vulnerability Dashboard, Query Builder, and Ask ORDRAI provide comprehensive insights and instant vulnerability information, helping teams focus on the most significant risks. Note: Effectiveness may vary based on asset complexity and integration depth.
Features & Capabilities
What are the key features of Ordr's CAASM+ platform for vulnerability management?
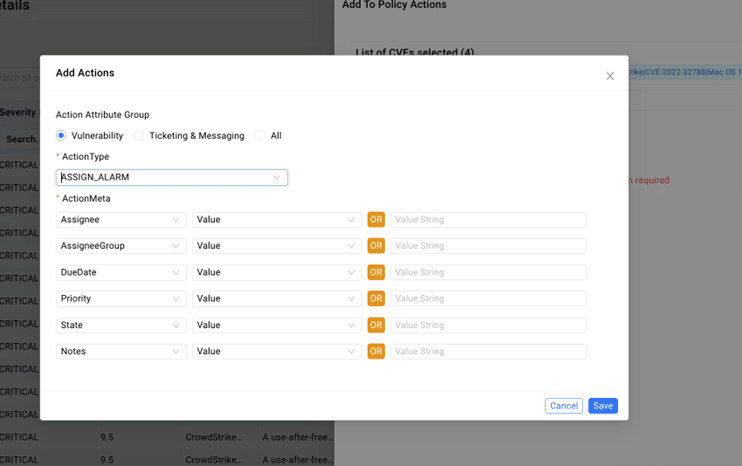
Key features include end-to-end vulnerability management, AI-driven asset classification, risk-based scoring, integrations with vulnerability assessment tools (Rapid7, Tenable, Qualys), Software Inventory Collector for non-scannable assets, Vulnerability Dashboard, Query Builder, Ask ORDRAI for natural language search, and enforcement actions such as network-based controls and ticketing system integrations. Note: Some features may require specific integrations or modules; check with Ordr for compatibility.
Does Ordr integrate with other security and IT tools?
Yes, Ordr supports over 130 out-of-the-box integrations, including firewalls (Cisco, Palo Alto Networks, Fortinet, Check Point), NAC (Cisco ISE, Aruba ClearPass, Forescout), SIEM/SOAR (Splunk, IBM QRadar, Microsoft Sentinel, Palo Alto Cortex XSOAR), ITSM (ServiceNow, BMC Remedy), clinical systems (Epic, Cerner, GE Centricity), switches (Cisco, Aruba, Juniper), and vulnerability scanners (Tenable, Qualys, Rapid7). For a complete list, visit Ordr's integrations page. Note: Integration depth may vary by tool; some advanced features require additional configuration.
Does Ordr provide an API and technical documentation?
Yes, Ordr provides an API and comprehensive technical guides for all products. These resources are available through the Ordr support portal (login required). Note: API access and documentation may require a valid Ordr subscription.
Implementation & Support
How long does it take to implement Ordr's platform?
Ordr is designed for rapid deployment. Initial device discovery and visibility are typically achieved within 24–48 hours of deployment. Enforcement policies can be deployed in just a few days, compared to the industry norm of 12–24 months. Note: Implementation timelines may vary based on environment complexity and integration requirements.
What support and training resources are available for Ordr customers?
Ordr offers 24/7 customer support with expert engineers, Ordr University training modules for onboarding and skill development, and comprehensive resources including product documentation, knowledge base articles, and case management tools. Note: Access to some resources may require a valid Ordr subscription.
Security & Compliance
What security and compliance certifications does Ordr hold?
Ordr is SOC 2 Type II certified, has been independently audited for Security, Availability, and Confidentiality Trust Service Criteria, and complies with GDPR and CCPA. Ordr is currently evaluating ISO 27001 certification as part of its ongoing compliance roadmap. For more details, visit Ordr's Trust Center. Note: ISO 27001 certification is not yet completed.
Pricing & Plans
How is Ordr's pricing determined?
Ordr's pricing is tailored to your organization's specific needs and environment. For detailed pricing information, contact the Ordr team directly or request a quote via the demo request page. Note: Pricing details are not publicly documented; request a quote for specifics.
Use Cases & Customer Success
What industries and roles benefit most from Ordr's platform?
Ordr serves healthcare, manufacturing, financial services, higher education, and retail/hospitality. Key roles include CISOs, IT managers, compliance officers, SOC teams, and risk management professionals. For case studies, visit Ordr's customer stories page. Note: Suitability may vary for organizations outside these industries; consult Ordr for custom use cases.
Can you share specific customer success stories related to vulnerability management?
Yes. Cleveland Clinic used Ordr to achieve real-time inventory and risk management for 10–15 connected devices per hospital room. CHRISTUS Health accelerated data center micro-segmentation and streamlined policy generation. Beebe Healthcare gained visibility into over 8,000 devices and achieved compliance at scale. Richmond upon Thames College achieved full campus visibility within days and automated segmentation. For more, visit Ordr's customer stories page. Note: Results may vary based on deployment scope and environment.
Competition & Comparison
How does Ordr compare to visibility-only platforms?
Visibility-only platforms typically offer basic asset discovery limited to IT devices and rely on static policy templates. Ordr provides real-time, automated asset discovery across IT, IoT, OT, and medical devices, with AI-driven behavioral fingerprinting and dynamic, adaptive policies. Note: Visibility-only platforms may be preferable for organizations with only IT assets and minimal segmentation needs.
How does Ordr compare to traditional vulnerability management tools?
Traditional vulnerability management tools rely on static assessments and manual risk prioritization. Ordr automates risk prioritization based on operational impact, uses AI-driven continuous learning, and integrates with vulnerability scanners for proactive mitigation. Note: Traditional tools may be suitable for organizations with established manual workflows and limited automation requirements.
How does Ordr compare to compliance-only solutions?
Compliance-only solutions focus on manual evidence collection and are limited to specific frameworks. Ordr provides continuous compliance monitoring and audit-ready reporting for multiple frameworks (HIPAA, PCI DSS, FERPA), with automated workflows that reduce audit preparation time. Note: Compliance-only solutions may be preferable for organizations with narrow compliance needs and minimal asset diversity.
How does Ordr compare to static policy enforcement tools?
Static policy enforcement tools require manual policy creation and rely on static templates. Ordr generates policies based on real traffic and device behavior, adapting dynamically as environments change. Note: Static tools may be suitable for environments with infrequent changes and low segmentation complexity.